 EN
An “Access denied” message can interrupt customer support, store management, or a client reporting task. But it does not always mean your IP address has been blocked.
The problem may involve account permissions, proxy authentication, a website security rule, excessive requests, or a network connection failure. Each requires a different response.
Before changing settings, record the error and identify where the failure occurs. For teams, a consistent troubleshooting process helps restore authorized access without disrupting other members’ work.
Start with the exact message shown by the website or browser.
A status code helps narrow the investigation, but it may not identify the complete cause. For example, a 403 response alone does not establish that the restriction is based on your IP.
Several issues can affect normal team workflows.
Shared network activity. Multiple employees or tools may use the same public connection. Their combined activity can reach a service’s request limit.
Incorrect proxy configuration. An expired subscription, incorrect credentials, or an unsupported connection setting can prevent a browser environment from reaching the internet.
Permission changes. A team member may lose access after a role update, an expired invitation, or a change to a client’s account settings.
Website security rules. A security service may reject a request that the website owner needs to review.
Background automation. A scheduled task, extension, or integration may continue sending requests after the operator stops interacting with the page.
Service availability rules. Some destinations restrict access by account eligibility, region, or contractual conditions. A connection change does not resolve those requirements.
Record:
The affected website and page.
The time and timezone.
The exact error message.
Any request ID or Ray ID shown.
The browser profile involved.
Whether one member or several members are affected.
Whether the problem began after a configuration change.
Take a screenshot, but remove customer information, credentials, and other sensitive details before sharing it.
Avoid changing the proxy, clearing cookies, and resetting the profile all at once. Multiple simultaneous changes make the cause harder to identify.
Determine whether the issue affects:
One website or several unrelated websites.
One browser profile or multiple profiles.
One account or several authorized accounts.
One employee or the entire team.
If unrelated websites also fail to load, start with connectivity and proxy configuration. If only one destination fails, examine that service’s status, permissions, and error message.
Use an approved test environment where possible. Do not create replacement accounts to continue using a suspended service.
If the browser profile uses a proxy, verify its address, port, protocol, and authentication method against the provider’s instructions.
Also confirm that the service is active and that any required IP authorization is current.
A successful proxy connection check establishes connectivity for that check. It does not prove that every destination will accept the resulting traffic.
For a 407 error, focus on proxy authentication rather than assuming the website has banned the account.
If the proxy itself is unavailable, ask the provider to resolve the connection issue. Keep any necessary configuration changes documented so other team members know which environment to use.
For a 429 response, stop repeated retries and inspect the task that generated them.
If the service provides a Retry-After instruction, follow it. For approved API integrations, use the documented rate limits and appropriate retry behavior.
Check for duplicated schedules, multiple workers performing the same task, or extensions refreshing pages in the background.
Rotating IP addresses to continue the same request volume does not resolve the underlying workload problem.
Confirm that the employee is signed in to the intended account and has the role required for the task.
For client accounts, ask the client administrator to review invitations, business permissions, and access expiry. A browser environment cannot grant permissions that the platform has not assigned.
If the platform shows a suspension or verification notice, use its official resolution process. Keep that investigation separate from ordinary network troubleshooting.
When contacting the website owner or support team, provide the affected URL, timestamp, error message, and request identifier.
For Cloudflare Error 1020, the website owner can investigate the security event. Visitors should provide the error screenshot and relevant details rather than repeatedly trying new connection settings.
If the affected website belongs to your organization, have the responsible administrator review security logs and the matching rule. Any adjustment should address the identified issue rather than broadly disabling protection.
Changing a DNS resolver does not, by itself, change the public source IP used for your connection.
DNS helps translate a domain name into the address needed to reach the destination. A source-IP restriction is a different mechanism.
DNS troubleshooting can help when name resolution is failing. It should not be presented as a method for removing a website’s IP restriction.
Likewise, clearing cookies may affect a login session, but it does not automatically remove a network-level block.
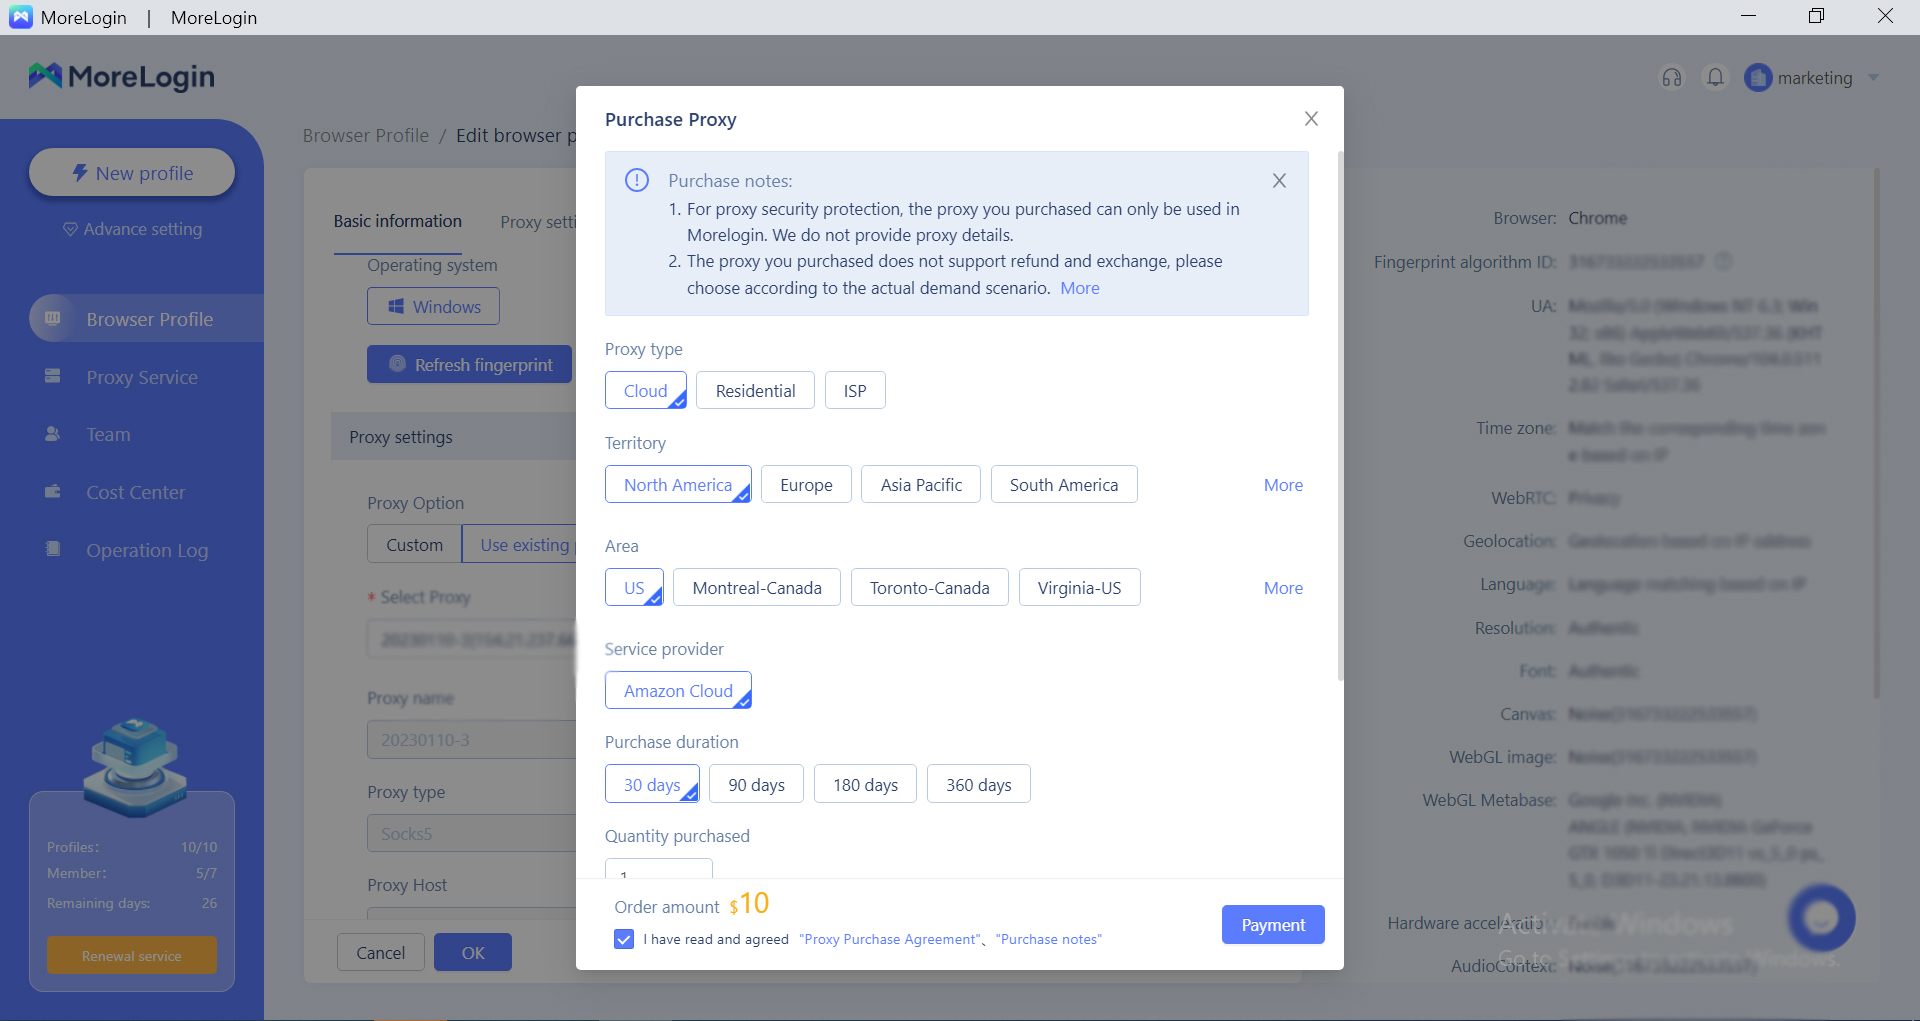
MoreLogin helps teams organize browser environments and apply controls to assigned workspaces. Its role in this process is to make configuration and access easier to manage.
Use consistent profile names and assignments so employees know which workspace belongs to each client or business task.
Separate browser profiles keep cookies and local storage apart. This helps reduce session mix-ups when employees work across several authorized accounts.
Maintain a record of the intended proxy configuration and the person responsible for changes. That makes troubleshooting easier when a connection stops working.
MoreLogin’s URL allowlists and blocklists let administrators define permitted or restricted destinations within configured browser environments.
For example, a reporting workspace can be limited to the websites needed for that assignment.
If a member cannot open a page, check these internal rules as part of troubleshooting. An organization’s own access restriction should not be mistaken for a block imposed by the destination website.
Custom security templates can apply selected page-element restrictions and controls over copying, uploads, downloads, and printing to assigned members and environments.
A team can use these controls to restrict an operation that is outside a member’s responsibility. Natural-language assistance can help identify the relevant page element during configuration.
Test templates with the intended role before applying them broadly. If a legitimate task stops working, review the template alongside the platform’s own permissions.
These controls govern the configured browser workflow. They do not change a website’s security rules, remove an IP block, or replace official account authorization.
After access is restored, document the actual cause and the change that resolved it.
For recurring team workflows:
Assign an owner for proxy and profile configuration.
Review permissions when responsibilities change.
Remove unused scheduled tasks and integrations.
Follow published request limits.
Keep a short record of configuration changes.
Test updated webpage restrictions before wider rollout.
The objective is to make authorized work predictable and easier to support.
No. It can result from permissions, security rules, account restrictions, or other conditions. Use the exact error message and available logs to identify the cause.
No. MoreLogin can help organize browser environments, proxy settings, and team controls, but the destination service determines its access restrictions.
First determine whether the proxy connection is the problem. Unnecessary changes can complicate diagnosis and disrupt established workflows.
They may share a network connection, proxy, account dependency, or internal access rule. Investigate shared components before treating each incident separately.
Different profiles can have different sessions, permissions, proxy settings, or internal rules. Compare those differences systematically; the result alone does not identify an IP block.
Use the platform’s official review or appeal process. Browser settings and replacement connections do not resolve the underlying account decision.
Start with the error, establish its scope, and correct the relevant connection, permission, or workload issue.
For teams using MoreLogin, clearly assigned environments and tested security templates can make that process easier to manage. They support organized operations while the website owner or platform remains responsible for its own access decisions.
 EN